
By NextGenTechNews Staff
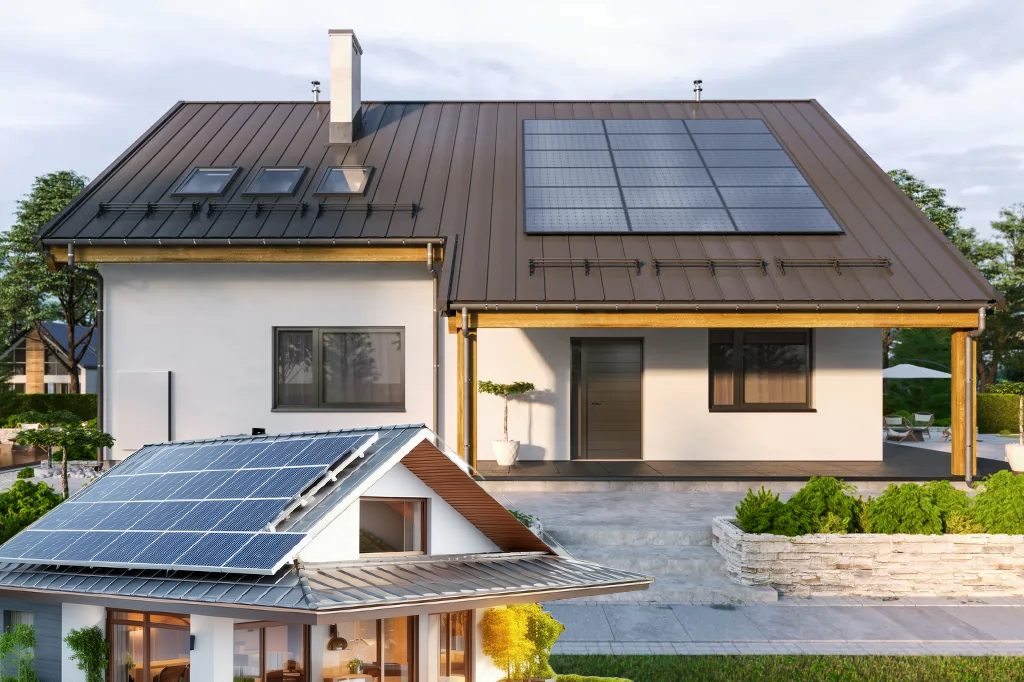
Imagine this: someone parks outside your home, cracks your Wi-Fi password, and starts tampering with the small gray box mounted near your garage — your solar inverter. This device quietly converts the direct current (DC) generated by your rooftop solar panels into alternating current (AC) that powers your appliances. Now, in the wrong hands, it could become a security threat.
That scenario, though unlikely, illustrates the potential dangers highlighted by a recent U.S. Cybersecurity and Infrastructure Security Agency (CISA) advisory. The agency flagged multiple vulnerabilities in solar inverters manufactured by EG4 Electronics, a Texas-based company. According to CISA, the flaws could allow an attacker with access to the same network and the inverter’s serial number to intercept data, install malicious firmware, or even take full control of the system.
Growing Concerns for Solar Homeowners
For the 55,000+ homeowners who own the affected EG4 inverter models, this news was unsettling. Many had never considered their solar inverter to be more than a simple power converter. In reality, modern inverters have evolved into the central nervous system of home energy setups. They monitor performance, communicate with utilities, and even feed excess power back into the grid.
“Five years ago, nobody even knew what a solar inverter was,” says Justin Pascale, a consultant at industrial cybersecurity firm Dragos. “Now, we’re discussing them at both national and international levels.”
The U.S. solar industry’s rapid growth has fueled these concerns. According to the U.S. Energy Information Administration (EIA), residential solar installations increased more than fivefold between 2014 and 2022. Each installation strengthens energy independence but also adds another digital access point that could be exploited.
Industry-Wide Weaknesses
EG4’s CEO, James Showalter, admits the security issues are real but argues they’re not unique to his company. “This is an industry-wide problem,” he says, pointing to more than 80 documented solar energy vulnerabilities since 2019.
Yet many customers were not impressed. Some complained on forums like Reddit after CISA revealed basic design flaws:
-
Unencrypted communication between apps and inverters
-
Firmware updates without integrity checks
-
Weak authentication protocols
“These were fundamental lapses,” said one EG4 customer, who requested anonymity. “To make it worse, the company never notified me or suggested fixes.”
Showalter calls the delay in communication a “live and learn” moment, claiming EG4 wanted to resolve issues before alarming customers.
CISA has clarified that no active exploitation of these vulnerabilities has been reported. Still, the warning shines a spotlight on broader risks in the renewable energy sector.
International Supply Chain Risks
Complicating matters are geopolitical concerns. Earlier this year, U.S. energy officials began reassessing risks tied to equipment manufactured in China. A Reuters investigation found undocumented communication components inside inverters and batteries from multiple Chinese suppliers.
Given that Huawei, Sungrow, and Ginlong Solis — all Chinese companies — dominate the global inverter market, the discovery was significant. In Europe, more than 200 gigawatts of solar capacity is tied to Chinese-made inverters, roughly equivalent to over 200 nuclear power plants.
Countries are responding. Lithuania, for instance, banned remote Chinese access to solar, wind, and battery installations above 100 kilowatts. EG4, meanwhile, says it is moving away from Chinese suppliers in favor of German-made components.
The Bigger Picture: A Distributed Attack Surface
The real danger lies not in individual hackers targeting single homes but in the aggregate vulnerability of thousands of interconnected systems. The National Institute of Standards and Technology (NIST) warns that a coordinated attack on a large number of inverters could disrupt the power grid for an extended period.
Pascale notes that while residential inverters primarily convert electricity and manage grid connections, a mass-scale compromise would require targeting manufacturers themselves — many of which maintain remote access to customer devices.
Currently, U.S. cybersecurity regulations cover only large facilities producing 75 megawatts or more, such as solar farms. Residential systems fall below these thresholds, leaving manufacturers largely free from strict oversight.
EG4’s Response and Path Forward
Showalter insists that EG4 is taking the CISA findings seriously. Since June, the company has been working closely with the agency, reducing the initial list of 10 security issues to just three, with full resolution expected by October. Planned fixes include:
-
Encrypted firmware transmission
-
Stronger identity verification for support calls
-
Improved authentication protocols
He calls this process a “trust upgrade” — a chance to strengthen EG4’s reputation in a competitive market.
But not all customers are convinced. Many solar adopters thought they were investing in clean energy solutions, only to find themselves exposed to complex cybersecurity issues they never imagined.
Looking Ahead
The shift toward distributed energy systems is accelerating, and with it comes a new wave of digital risks. Each solar inverter installed on a home contributes not just to energy independence but also to a growing attack surface for potential cyber threats.
While government agencies and manufacturers scramble to improve defenses, homeowners remain caught in the middle — beneficiaries of renewable technology but also unwilling participants in a broader cybersecurity challenge.
As Pascale puts it: “The real concern isn’t today’s isolated risks, but what happens as millions more inverters come online. The stakes only get higher.”
